The NIS2 directive: What’s at stake?
In force since October 2024 across all 27 EU member states, the NIS2 Directive raises the cybersecurity baseline for essential and important sectors, ranging from energy and healthcare to manufacturing and digital infrastructure.
For OEMs and system integrators, compliance is no longer optional. It’s a strategic imperative.
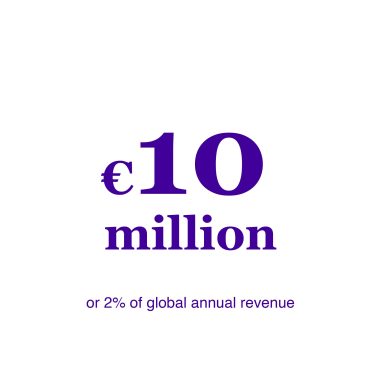
Non-compliance can mean penalties up to €10 million or 2% of global annual revenue, and—more critically—loss of customer trust and disrupted operations.
Who does it affect?
NIS2 extends its reach to cover a greater number of sectors and types of companies compared to NIS1. This includes entities operating in “High Criticality Sectors” and “Additional Critical Sectors”, provided they meet certain size criteria. Industries affected by the NIS2 include:


What does NIS2 require?
NIS2 takes a holistic approach, combining legal responsibility with technical resilience. Explore the key topics below.
Why it matters for industrial stakeholders
According to the Clusit Report 2024, cyberattacks against the manufacturing sector grew by 25% in the past year, with 4 out of 5 incidents classified as high or critical severity.
Moreover, 47% of global hacktivist attacks in 2023 targeted Italy, underlining the need for proactive cyber resilience in the industrial fabric.
How Eurotech supports NIS2 compliance
At Eurotech, we embed security-by-design in every product and platform we build. Here’s how we help.

CERTIFIED EDGE PLATFORMS:
IEC 62443-4-2 aligned gateways and edge AI devices, designed for secure OT/IT convergence.


SECURITY-BY-DESIGN AND ANTI-TAMPER PROTECTION:
Our hardware and software are developed with Zero-Trust principles at the heart. Eurotech’s industrial-grade IoT gateways and edge devices are built with anti-tampering features, hardware root of trust, and secure boot to guarantee device integrity from the factory.
INTEGRATED MONITORING AND ALERTING:
Eurotech devices provide continuous protection from physical and logical attacks with a unique tamper detection system that works even when devices are disconnected33. This is complemented by Intrusion Detection and Prevention Systems (IDS/IPS) and flawless Over-The-Air (OTA) updates, combinable with Everyware Cloud for remote configuration management and continuous monitoring of your edge fleet.
LIFECYCLE VULNERABILITY MANAGEMENT:
From deployment to decommissioning, our tools ensure traceability and update integrity.
SUPPLY CHAIN ASSURANCE:
We have a development process that ensures proactive assessment of the Software Bill of Material, and along with the continuous vulnerability monitoring. We help assess and secure third-party dependencies through vendor validation and integration best practices.
Trusted technology partner
With over 30 years of experience and a track record of achieving industry-benchmark certifications, Eurotech is a partner you can trust to build secure, compliant solutions tailored to your specific needs.
THE BOTTOM LINE
With NIS2, the EU has signaled that cybersecurity is a non-negotiable component of critical infrastructure. For OEMs and integrators, it’s an opportunity: not just a mandate.
Be ready. Be resilient. Be a trusted partner.
Start your NIS2 journey today.